FBI Malware Warning: Millions Affected
- The FBI has issued a warning regarding BADBOX 2.0, a malware strain rapidly spreading through consumer electronics.
- BADBOX 2.0 can pilfer your data and create backdoor access to infected devices, making removal extremely tough.
- BADBOX 2.0 is an evolution of the original BADBOX malware,first identified in 2023.
The FBI alerts consumers: BADBOX 2.0 malware is infecting millions of internet-connected consumer devices, from smart TVs to streaming boxes. This refined botnet steals data and grants backdoor access, posing a significant cybersecurity threat. Pre-installed on many devices, especially those from China, this malware activates upon network connection, turning your devices against you. The evolution of the original BADBOX,this iteration is proving especially difficult to eradicate. read our latest from News Directory 3 to understand how it effectively works,the scope of the threat,and how to protect your home network. Discover what’s next for countermeasures and the evolving threat landscape.
FBI Warns of BADBOX 2.0 Malware infecting Consumer Devices
The FBI has issued a warning regarding BADBOX 2.0, a malware strain rapidly spreading through consumer electronics. Millions of internet-connected devices are now infected with this malware, which is frequently enough preloaded onto inexpensive streaming hardware and IoT devices.
BADBOX 2.0 can pilfer your data and create backdoor access to infected devices, making removal extremely tough. this malware represents a important threat to home network security.
BADBOX 2.0 is an evolution of the original BADBOX malware,first identified in 2023. Although a German cybersecurity agency disrupted the original malware by sinkholing communications between infected devices, it wasn’t fully eradicated. Now, BADBOX 2.0 has resurfaced, creating a massive botnet.
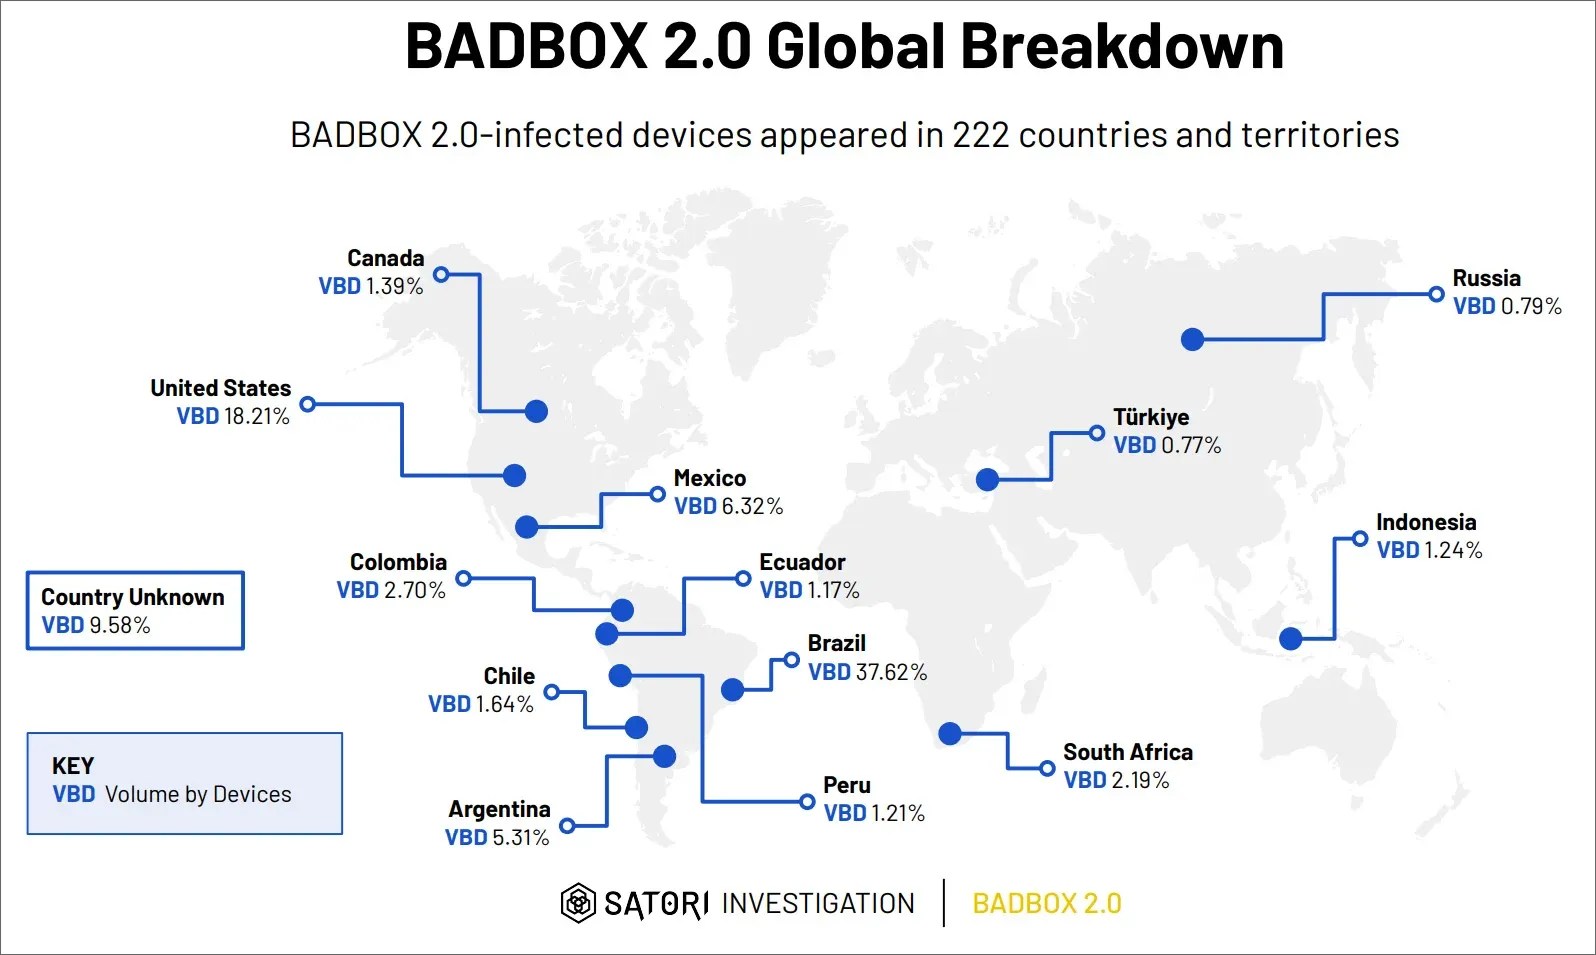
The BADBOX 2.0 botnet now encompasses over one million devices, including smart TVs, IoT gadgets, streaming boxes, projectors, and tablets. The FBI’s public service announcement highlights that many devices are pre-infected with the malware at the point of sale, primarily originating from China.
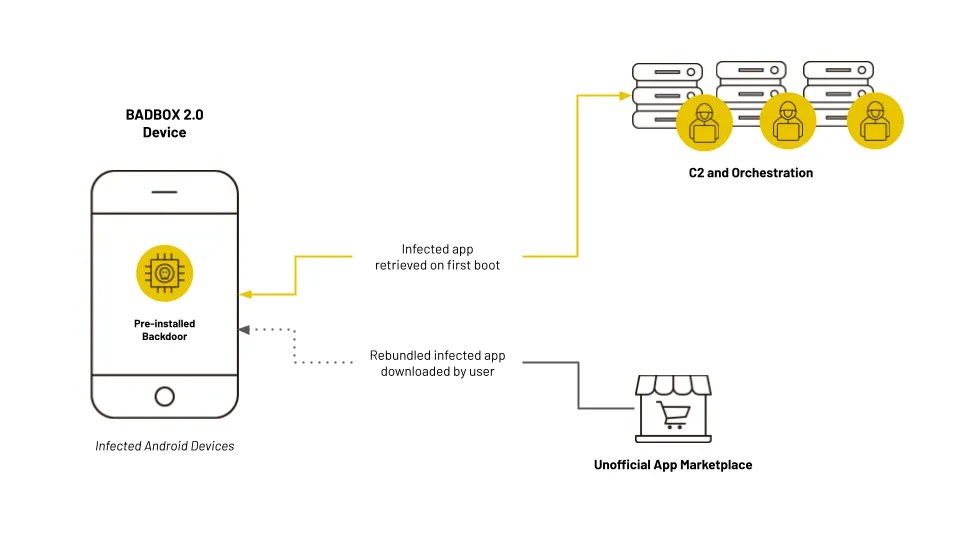
Cyber criminals gain unauthorized access to home networks by either configuring the product with malicious software prior to the users purchase or infecting the device as it downloads required applications that contain backdoors, usually during the set-up process.
Once an infected device connects to a network, it “phones home” to a control network, activating the BADBOX 2.0 malware. The device then becomes part of the botnet, frequently enough without any clear indication of infection.