
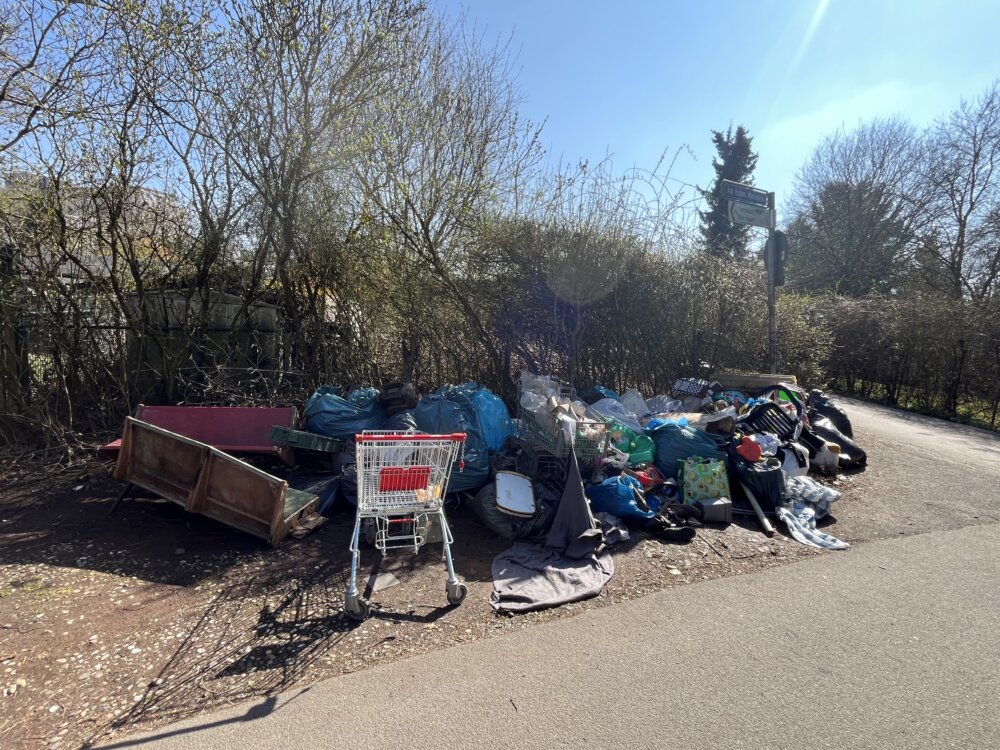
Frankfurt: Illegal Waste Disposal
- FRANKFURT, Germany – City officials in Frankfurt are appealing to the public for assistance in combating a growing problem of illegal waste disposal.
- Kraft, head of the city's waste management agency (ASE), stated that the situation has reached a critical point, necessitating public involvement.
- Authorities are reminding residents that illegally disposing of waste is a criminal offense.
Frankfurt Grapples with Illegal Waste Disposal, Authorities Seek PublicS Help
FRANKFURT, Germany – City officials in Frankfurt are appealing to the public for assistance in combating a growing problem of illegal waste disposal. The surge in improperly discarded refuse has prompted the authorities to take action, emphasizing the financial burden it places on the community.
Michaela C. Kraft, head of the city’s waste management agency (ASE), stated that the situation has reached a critical point, necessitating public involvement. Residents are reminded that the Frankfurter Entsorgungs- und service GmbH (FES) offers free disposal options for bulky and garden waste, either through drop-off or scheduled pick-up services.
Penalties for Illegal Dumping
Authorities are reminding residents that illegally disposing of waste is a criminal offense. Under Paragraph 326 of the Criminal Code, those caught illegally dumping waste, or attempting to do so, face penalties of imprisonment for up to five years or considerable fines.
Community Duty
waste disposal is an individual responsibility, officials emphasize. When individuals illegally dispose of waste, the consequences are borne by the entire community, resulting in meaningful costs for the general public.
Resources for Proper Waste Disposal
For detailed information on proper waste disposal procedures, residents can visit fes-frankfurt.de. Inquiries can also be made by phone at 0800/200-800-70.
Website Privacy Settings: Understanding Your Choices
Websites commonly use cookies and similar technologies to enhance user experience. These technologies process personal data, such as IP addresses, to personalize content and advertisements, integrate third-party media, and analyze website traffic. This data processing may occur as a direct result of setting cookies. This information is often shared with third parties, as outlined in the privacy settings.
Data processing can occur based on user consent or legitimate interest. users have the right to object to processing based on legitimate interest within the privacy settings. You retain the right to withhold consent and to modify or revoke your consent at a later time. Further details regarding the use of your data can be found in the website’s privacy policy.
Privacy Options
Users are typically presented with several options regarding their privacy preferences:
- Except All: This option signifies agreement to all data processing purposes.
- continue Without Consent: This allows users to proceed without providing explicit consent, possibly limiting certain website features.
- Individual Privacy Settings: This provides granular control over which data processing activities are permitted.
Data Processing in Unsafe third Countries
some services may process personal data in countries with less stringent data protection laws. By consenting to the use of these services, users agree to the processing of their data in these countries, acknowledging the potential risks. These risks include the possibility of government access to data for monitoring purposes without the availability of legal recourse.
Age Restrictions
users below a certain age (e.g., under 16) may be restricted from consenting to optional services. In such cases, parental or guardian consent may be required.
Service Overview
Accepting all services typically allows the loading of various functionalities, frequently enough categorized by purpose. Some services might potentially be loaded based on legitimate interest, while others require explicit consent.
Custom Services Outside TCF Standard
Certain services may not adhere to the Transparency and Consent Framework (TCF) standard, instead relying on alternative technologies for consent management. These services are categorized by purpose, with some utilized based on legitimate interest (e.g., security) and others requiring user consent. Detailed information about each service’s purpose can be found in the individual privacy settings.
Consent Scope
User consent may extend to multiple websites.
Blocked Content
Privacy settings may block certain content. Users can adjust their settings to unblock content and prevent future blocking from the same service.
Managing Your Privacy
Users can typically access a history of their privacy settings,revoke consent,or modify their preferences at any time.
Individual Privacy Settings
Websites provide an overview of all services used, allowing users to view detailed information and individually consent to or object to each service.
Note: This information is for general understanding and may vary depending on the specific website’s privacy practices. Always refer to the website’s privacy policy for complete details.
Website Cookie and Consent Management: A Detailed Overview
Websites employ various technologies to enhance user experience, ensure security, and comply with data privacy regulations. These technologies often involve the use of cookies and require obtaining user consent for data processing. This article examines several services and tools commonly used for these purposes.
Real Cookie Banner: Consent Management Platform
The Real Cookie Banner is a consent management platform (CMP) designed to obtain website visitors’ consent for setting cookies and processing personal data. According to rhein Main Verlag, the provider of Real Cookie Banner, each visitor is assigned a universally unique identifier (UUID) for consent tracking purposes.This UUID remains valid until the cookie expires.
Cookies are used to verify cookie functionality,store references to documented consent,and record user preferences regarding services and service groups. When consent is obtained under the Transparency & Consent Framework (TCF), the platform stores user agreements with TCF partners, purposes, special purposes, functions, and special features.
As part of data protection obligations under the General Data protection Regulation (GDPR), the collected consent is fully documented. This documentation includes the services and service groups the visitor has consented to, and if consent is obtained under the TCF standard, the TCF partners, purposes, and functions the visitor has agreed to. All cookie banner settings at the time of consent,technical circumstances (e.g., viewport size), and user interactions (e.g., button clicks) leading to consent are also recorded. Consent is obtained separately for each language.
Technical Definitions of Cookies Used by Real Cookie Banner:
- real_cookie_banner*: A unique identifier for consent, not the website visitor. It includes a revision hash for cookie banner settings and IDs for consented services and service groups. Duration: 365 days.
- real_cookie_banner*-tcf: Stores TCF-collected consents in TC-String format, including TCF vendors, purposes, special purposes, functions, and special features. Duration: 365 days.
- real_cookie_banner*-gcm: Stores Google Consent Mode consents for various consent types (purposes) for all Google Consent Mode-compatible services.Duration: 365 days.
- real_cookie_banner-test: A temporary cookie used to test HTTP cookie functionality, deleted instantly after the test. Duration: 365 days.
- real_cookie_banner* (local): A unique identifier for consent, stored locally until consent is documented on the website server. Duration: 1 day.
- real_cookie_banner*-tcf (local): Locally stores TCF-collected consents until documented on the server. Duration: 1 day.
- real_cookie_banner*-gcm (local): Locally stores Google Consent Mode consents until documented on the server. Duration: 1 day.
- real_cookie_banner-consent-queue*: Caches cookie banner selections locally until the server documents the consent. Documentation is attempted periodically or on page changes if the server is unavailable or overloaded. Duration: 1 day.
For further information, refer to the Rhein Main Verlag privacy policy.
Functional Services and Third-Party Integrations
Functional services enhance website features beyond core functionality, such as improved fonts, video playback, and interactive Web 2.0 features. Content from video and social media platforms is typically blocked by default and requires user consent to load.
Issuu
Issuu allows embedding content published on issuu.com directly into websites. According to Issuu, Inc., cookies are used to collect data on visited web pages and detailed user behavior statistics. This data may be linked to registered users on issuu.com.
Technical Definitions of Cookies Used by issuu:
- mc: Cookie from quantserve.com. Duration: 25 months.
- d: Cookie from quantserve.com. Duration: 3 months.
- iutk: Cookie from issuu.com. Duration: 6 months.
For more details, see the Issuu privacy policy.
Google reCAPTCHA
Google reCAPTCHA, provided by Google Ireland Limited, is used to detect bots and prevent spam, notably in online forms. Cookies identify users within Google’s known data and classify user behavior. This data can be linked to users logged into their Google accounts.
Technical Definitions of Cookies Used by Google reCAPTCHA:
- NID: Cookie from google.com. Duration: 1 year.
- rc::a, rc::b, rc::c: Local cookies from google.com. Duration: 1 second.
- SIDCC: Cookie from google.com. Duration: 1 year.
- __Secure-3PAPISID, SSID, SAPISID, APISID, HSID, SID, __Secure-3PSID: Cookies from google.com.Duration: 2 years.
- SEARCH_SAMESITE: Cookie from google.com.Duration: 6 months.
- CONSENT: Cookie from google.com. Duration: 18 years.
- 1P_JAR: Cookie from google.com. duration: 1 month.
Refer to the Google privacy policy for more information.
Cloudflare
Cloudflare, provided by Cloudflare Inc., protects websites from malicious traffic and caches website content for faster delivery. It can also serve a cached version of the webpage if the website’s server is unavailable. Cookies are used to uniquely identify users, classify potential attackers, and determine the fastest available server.
Technical Definitions of Cookies Used by Cloudflare:
- _cflb: Cookie from rheinmainverlag.de. Duration: Session.
- _cf_bm: Cookie from rheinmainverlag.de. Duration: 30 minutes.
- cf_ob_info, cf_use_ob: Cookies from rheinmainverlag.de. Duration: 1 minute.
- __cfwaitingroom: Cookie from rheinmainverlag.de. Duration: 1 day.
See the Cloudflare privacy policy for details.
Okay, I understand. I will analyze the provided text,rewrite it into a professional news article adhering to AP style and semantic HTML5 standards,and focus on originality to minimize plagiarism risks. I will also ensure a natural, human-like quality and vary sentence structure and vocabulary.
Please provide the article text. I’m ready to begin.
Website integrations: Facebook, OneSignal, gravatar, google Fonts, and analytics
This article outlines several third-party services commonly integrated into websites, detailing their purpose, data handling practices, and privacy implications.
Facebook Integration
Websites frequently enough integrate Facebook for various functionalities. this integration involves setting local cookies on users’ browsers, including “_cs_marauder_session_id,” “_cs_marauder_last_session_id,” “_cs_marauder_last_event_time,” ”JewelBase:count-updated,” “channel_sub:*,” “ps:,” “_oz_bandwidthAndTTFBSamples,” ”_oz_bandwidthEstimate,” and “banzai:last_storage_flush.” These cookies, hosted on www.facebook.com, typically have a duration of zero years and are not session-specific.
The integration’s purpose is unspecified in the provided data. Facebook’s privacy policy is available at https://www.facebook.com/about/privacy.
The integration uses a base64-encoded script to create a Facebook root div and load the Facebook SDK asynchronously. This script includes a cross-origin attribute and a nonce for security.
OneSignal Push Service
OneSignal is used to send push notifications to subscribed users. The service, provided by OneSignal, processes data in the United States.A technical definition includes an HTTP request to onesignal.com with a duration of seven days.
OneSignal’s privacy policy can be found at https://onesignal.com/privacy.
Gravatar (Avatar Images)
gravatar, provided by Automattic Inc., allows users to associate their email addresses with avatar images, frequently enough displayed in comment sections. While Gravatar doesn’t set cookies on the user’s client, it transmits technical and personal data, such as IP addresses, to its servers to enable the service.
Automattic’s privacy policy is available at https://automattic.com/privacy/.
Google Fonts
Google Fonts, provided by Google Ireland Limited, downloads and embeds fonts not installed on the user’s device. Similar to Gravatar, Google Fonts does not set cookies but transmits technical and personal data, including IP addresses, to Google’s servers.
Google’s privacy policy is available at https://policies.google.com/privacy.
The integration uses a script to handle Web Font Loader compatibility, attempting to load fonts from Typekit or Google Fonts. It iterates through modules and handles them individually, unblocking them and then calling the original WebFont.load function.
Website Statistics with Google Analytics
Statistical services, such as Google Analytics, are used to collect pseudonymized data about website visitors. This data helps website operators understand their audience and optimize the website.
google Analytics Details
Google Analytics, provided by Google Ireland Limited, creates detailed statistics about user behavior on the website. This involves processing IP addresses and metadata to determine a user’s country, city, and language. Cookies or similar technologies may be stored and read, potentially containing personal and technical data such as user IDs.
The data collected includes:
- Time information about when and how long a user was on different pages.
- Device category (desktop, mobile, tablet), platform (web, iOS app, Android app), browser, and screen resolution.
- Referral source (e.g., referring website, search engine, social media platform, newsletter).
- Whether a user belongs to a target group.
- User actions and events triggered by those actions (e.g., page views, user engagement, scrolling behavior, clicks, added payment information, and custom events like e-commerce tracking).
- Conversions (e.g., whether a user purchased something and what was purchased).
- Gender, age, and interests, if available.
Google may use this data to track visited websites and improve its services. The data might potentially be linked across multiple domains operated by the website operator and with other Google products (e.g., Google AdSense, Google Ads, BigQuery, google Play). It may also be linked with data from users logged into Google websites (e.g., google.com). Google shares personal data with its affiliates and trusted companies or individuals who process it on Google’s instructions and in accordance with Google’s privacy policy.
The data may also be used for profiling by the website operator and Google, such as to provide personalized services like ads based on user interests or recommendations.
Facebook Integrations Raise Privacy Concerns Over Data Sharing
Dublin, Ireland – Meta Platforms ireland Limited, the European headquarters of Facebook, faces scrutiny over its data-sharing practices related to website integrations like “Like,” “Share,” and comment plugins. These integrations,designed to enhance user engagement,collect user data that is then shared globally within Meta’s internal network and with external partners,measurement services,and other third-party providers.
Data Collection and Usage
The integrations function by embedding buttons and comment sections into websites,potentially improving user experience. however, this process involves collecting user IP addresses and metadata. Cookies and similar technologies may also be stored and accessed,containing personal and technical data such as user IDs,button sizes,and software versions.
According to Meta’s documentation, this data can be used to track visited websites, generate detailed user behavior statistics, and improve Meta’s services. Furthermore, the information may contribute to user profiling, enabling personalized services like targeted advertising and content recommendations. Meta may link this data with information from users logged into Facebook and Instagram, utilizing both automated systems and manual reviews to process user data.
Global Data transfer
Meta acknowledges that collected information is shared worldwide, encompassing internal transfers within its offices and data centers, as well as external transfers to partners, measurement service providers, service vendors, and other third parties. The company lists the United States,Ireland,Singapore,Denmark,and Sweden as locations were data processing occurs.Meta also claims self-certification under the Trans-Atlantic Data Privacy Framework.
Technical Details: Cookies and Storage
Several HTTP cookies are associated with these Facebook integrations,each with varying durations and purposes:
c_user: Stores user ID information for one year.xs: Stores session information for one year.datr: Used for security purposes, lasting 13 months.dpr: manages display density, lasting seven days.wd: Tracks browser window dimensions for seven days.sb: used for browser identification, lasting 13 months.oo: tracks opt-out preferences, lasting 13 months.
Other Integrations and Providers
Besides the core “Like,” “Share,” and comment plugins,other integrations like the Facebook Page plugin also raise similar privacy considerations. The Page Plugin displays information about Facebook pages and may collect data about visited websites, potentially linking this data to logged-in Facebook users.
Quantcast, an audience insights and advertising platform, also features in the data-sharing landscape. Quantcast uses the “Quantcast” cookie, which lasts for one year and is used for identification purposes.
Legal Basis and User Consent
Meta states that the legal basis for data processing related to these integrations is user consent. Users are advised to review Meta’s privacy policy for thorough information on data usage and their rights.
For further inquiries, users can contact Meta’s support team via email at support@fb.com or visit their business help center.
This report is based on publicly available information and documentation from Meta Platforms Ireland Limited.
Taboola Tracks User Data for Personalized Content, advertising
NEW YORK (AP) — Taboola, a content suggestion platform, collects user data to personalize content and advertising, according to information on the Rhein Main Verlags gmbh website. the data gathered includes IP addresses, operating system details, browser information, accessed pages, event information like system crashes, and general location data such as city and country.
This information is used to tailor content and advertisements to the interests of website visitors. Taboola also creates a profile of website visitors that spans across different browsers and devices.
Data Sharing Practices
Taboola shares the collected data with affiliated companies, service providers, non-affiliated companies for advertising optimization, and website operators. this data sharing is intended to improve the relevance and effectiveness of the advertising displayed to users.
Use of Cookies
Cookies are employed to distinguish users through unique identifiers and to track their behavior on websites. This detailed tracking helps Taboola avoid showing duplicate recommendations, remember user actions within the “Taboola Select” feature, and recall which articles recommended by Taboola have been clicked.
The cookies also serve to remember when recommendations have been customized for a specific user, facilitate the use of the Taboola Newsroom service, and optimize ad delivery. For example, the referring website is stored, and the performance of clicked articles is measured.
Additionally, a technical identification number is used to enhance Taboola’s browser-based and mobile SDK services.
Specific Cookies and Their Functions
Several types of cookies are used by Taboola, including:
taboola_session_id: A session cookie used for tracking user sessions.taboola_select: A cookie that remembers user actions in the “Taboola Select” feature, with a duration of one year.taboola_fp_td_user_id: A cookie that identifies users, lasting for one year.t_gid: Another cookie used for user identification, also with a one-year duration.trc_cookie_storage: A cookie associated with the Rhein Main Verlags GmbH website, lasting one year._tb_sess_rand_tb_t_ppg: Cookies with a duration of 30 minutes.abLdr: A cookie with a duration of 3 hours.tb_click_param: A cookie that lasts for 50 seconds.
Privacy and Legal Information
Taboola’s privacy policy can be found at https://www.taboola.com/de/policies/datenschutzerklaerung.The company is headquartered in New York City.
Rhein Main Verlags GmbH, located in Obertshausen, germany, operates the website where this information was disclosed.Their contact information is available on their website.
Cookie Consent Management: A Deep Dive into Services and Regulations
Navigating the complexities of cookie consent management requires a comprehensive understanding of the various services involved and the regulations governing their use. This article examines several key services and frameworks that websites utilize to ensure compliance with privacy laws.
Essential Services for Compliance
Several services play a crucial role in managing cookie consent and ensuring user privacy. These range from handling basic website functionality to more complex tracking and advertising technologies.
wordpress Emojis
WordPress emojis, identified by rules such as *s.w.org/images/core/emoji*, are a standard feature. These emojis enhance user experience but fall under scrutiny regarding data usage.
Facebook Embedded Posts
Embedded Facebook posts, governed by rules including *facebook.com/plugins/post.php*, integrate social media content directly into websites. These embeds frequently enough involve tracking and require user consent.
Facebook Page Plugin
The Facebook Page Plugin, with rules like *facebook.com/plugins/page.php*, allows websites to display a Facebook page. This integration necessitates consent due to potential data transfer.
MonsterInsights
MonsterInsights, identified by rules such as “G-*” and “*google-analytics.com/analytics.js*”, is a popular analytics tool for wordpress. It tracks website traffic and user behavior, requiring appropriate consent mechanisms.
Transmatico
Transmatico, identified by rules such as *trmads.eu*, is a service related to online advertising. its use necessitates user consent due to data collection practices.
OneSignal
OneSignal, governed by rules including *cdn.onesignal.com*, provides push notification services. These notifications require consent as they involve user engagement and potential data tracking.
Gravatar
Gravatar, identified by rules such as *gravatar.com/avatar*, provides globally recognized avatars. While seemingly innocuous, the service involves data transfer and is subject to consent requirements.
Google Fonts
Google Fonts, with rules like *fonts.googleapis.com*, delivers fonts to websites. Using Google Fonts can raise privacy concerns due to potential IP address logging, thus requiring consent consideration.
Taboola
Taboola, identified by rules such as *cdn.taboola.com*, is a content recommendation platform. Its use involves tracking user behavior and requires consent.
Regulatory Frameworks and Data Processing
Cookie consent management is heavily influenced by regulatory frameworks such as GDPR (General Data Protection Regulation) and DSG (Swiss data Protection Act). These regulations dictate how personal data must be handled and require explicit user consent for data processing.
The GDPR applies to countries within the European Economic Area (EEA), including Austria, belgium, Bulgaria, Croatia, Cyprus, Czech Republic, Denmark, Estonia, Finland, france, Germany, Greece, Hungary, Ireland, Iceland, Italy, Liechtenstein, Latvia, Lithuania, Luxembourg, Malta, Netherlands, Norway, Poland, Portugal, Romania, Slovakia, Slovenia, Spain, and Sweden.
The DSG governs data processing in Switzerland.
Adequacy decisions by the EU Commission recognize certain countries as providing adequate data protection. These include Andorra, Argentina, Canada (with limitations), Faroe Islands, Guernsey, israel, Isle of Man, Japan, Jersey, New Zealand, South Korea, Switzerland, the United Kingdom, Uruguay, and the United States (limited to the Data Privacy Framework).
Conclusion
Effective cookie consent management requires a thorough understanding of the services used on a website and the applicable regulatory frameworks. by implementing appropriate consent mechanisms and adhering to privacy regulations, websites can protect user privacy and maintain compliance.
Cookie Consent and Data privacy: A Closer Look
The digital landscape is increasingly shaped by discussions surrounding cookie consent, data privacy, and the mechanisms that govern them. Understanding these elements is crucial for both website operators and users navigating the internet.
Understanding Cookie Consent
Cookie consent refers to the process of obtaining permission from users before deploying cookies or similar technologies on their devices. This consent is often required by data privacy regulations, such as the general Data Protection Regulation (GDPR) in Europe.
Legal Basis for Data Usage
Several legal bases can justify the use of personal data. These include:
- Consent for processing personal data.
- consent for storing or accessing information on a user’s device.
- Legitimate interest in processing personal data.
- Legitimate interest in providing a specifically requested digital service.
- Fulfillment of a legal obligation to process personal data.
Data Processing in Third Countries
Data processing in countries outside the European Union (EU) or Switzerland raises specific concerns. Mechanisms like Standard Contractual Clauses,Adequacy Decisions,and Binding Corporate Rules are employed to ensure data protection during these transfers.
Google Consent Mode
Google Consent Mode is emerging as a standard for obtaining consent for data processing and cookie usage. It allows websites to adjust Google services based on user consent,offering personalized experiences when consent is granted and maintaining core functionality when it is not.
More information on data processing by Google and its partners can be found at Google’s privacy policy.
Non-Standard Data Processing
Some services may use cookies or process personal data without adhering to standard consent protocols. These services are often categorized into groups, with essential services relying on legitimate interest and requiring direct objection via email or letter, as outlined in the privacy policy.
Technical Cookie Definitions
Understanding the technical aspects of cookies is essential. Key elements include:
- Technical cookie name
- Cookies used
- Cookie refresh frequency
- Use of cookie-like information (LocalStorage,SessionStorage,IndexDB,etc.)
- Host
- Duration
- Type
- Purpose
Privacy Settings History
Users can often access a history of their privacy settings, allowing them to review and manage their consent choices over time.
The Importance of Transparency
transparency is paramount in the realm of data privacy. Providing clear and accessible information about data processing practices builds trust and empowers users to make informed decisions about their online activity.