
Simsim Data Not Encrypted: Experts Call for Security Regulations
- SEOUL, South Korea – SK Telecom is under pressure to bolster its security protocols following concerns that subscriber identity module (USIM) cards are vulnerable to hacking.
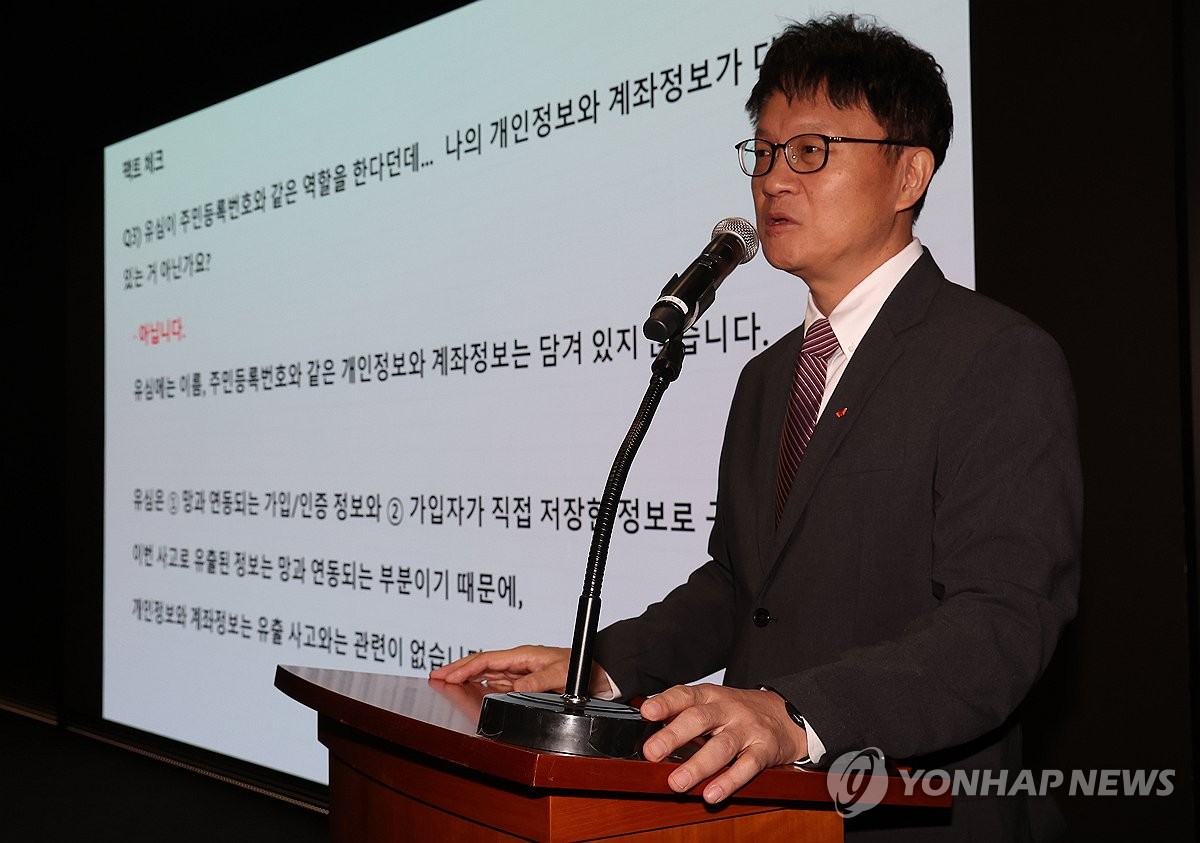
- ryu Jung-hwan, a vice president at SK telecom, addressed the National Assembly's Science and Technology Information and Communications Commission last month, acknowledging that the network is not fully...
- Current laws do not mandate encryption for subscriber identification numbers (IMSI) and subscriber authentication keys stored on USIM chips.
SK Telecom Faces Scrutiny over USIM Security After Hacking Concerns
Table of Contents
- SK Telecom Faces Scrutiny over USIM Security After Hacking Concerns
- SK Telecom USIM Security Under Scrutiny: Your Questions answered
- 1. What’s the Core Issue with SK Telecom’s USIM Security?
- 2. Why is Encryption Vital for USIM Data?
- 3. What Data is at Risk?
- 4. Has SK Telecom Been Hacked?
- 5. What Challenges Exist in Encrypting USIM Information?
- 6.What Do Experts Suggest to Improve Security?
- 7. What’s the Role of Legal Compliance in Addressing the Vulnerabilities?
- 8. Is SK Telecom Infrastructure Considered ‘Major Infrastructure’?
- 9. How Does Investment in Security Compare to Other Spending?
- 10. What’s the Impact of the ISun Data Harvest on the Broader Landscape?
- 11.What are the Specific Actions SK Telecom Is Taking?
- 12. In a Nutshell, What’s the Takeaway?
SEOUL, South Korea – SK Telecom is under pressure to bolster its security protocols following concerns that subscriber identity module (USIM) cards are vulnerable to hacking. Experts are calling for stricter regulations and increased investment in information security to protect user data.
Network Encryption Debate
ryu Jung-hwan, a vice president at SK telecom, addressed the National Assembly’s Science and Technology Information and Communications Commission last month, acknowledging that the network is not fully encrypted.”It was the same as the legal matters, but we are also very reflecting on that part,” Ryu stated.
Current laws do not mandate encryption for subscriber identification numbers (IMSI) and subscriber authentication keys stored on USIM chips.
The Personal Information Protection Committee stipulates encryption for only seven categories of personal information that processors must safeguard.
Growing Threat Landscape
The expansion of information technology has led to mobile carriers and platform companies collecting more data, creating more opportunities for hackers. A leaked internal document from Chinese security firm ISun revealed the company had harvested data from major telecommunications companies and government agencies through hacking.
Among the stolen data was 3 terabytes of LG Uplus customer call records, causing meaningful concern.
Inquiry and Encryption Challenges
The Ministry of Science and Technology, the National Intelligence Service (NIS), and the Korea Internet & Security Agency (KISA) investigated the alleged hacking incident to determine the extent of the data breach.
However, applying encryption to USIM information stored on carrier servers presents challenges, as this data is frequently accessed. Ryu stated in a briefing on May 2 that the core issue is that USIM information is not encrypted. “If there is a part that can be encrypted, we are making advisors to make measures,” he added.
Expert Opinions
Yeom Heung-yeol, a professor of information security at Suncheon Hyang University, noted the difficulties of encryption due to the need for real-time processing at the network stage. However, he believes partial encryption is becoming more feasible as computing performance increases.
We need to incorporate mobile carrier servers as government security analysis through the revision of the Information and Communication -based Protection Act or the Enforcement Decree.
Infrastructure Designation
According to data submitted by Democratic Party member Choi Min-hee, SK Telecom’s infrastructure, which was targeted in the hack, has not been designated as a major information and communication infrastructure requiring national protection.
An official from the Ministry of Science and Technology stated that the ongoing investigation into the SK Telecom case may lead to the designation of servers and other facilities as major infrastructure under the Information and Communication-based protection Act.
investment in Security
Critics argue that carriers need to increase thier investment in information protection. SK Telecom’s investments in information security totaled 60 billion won last year, while its subsidiary SK Broadband invested 26.7 billion won.These figures are dwarfed by the 136.7 billion won spent on marketing, including the use of the group New Jeans as a promotional model for the iPhone 16.
Yeom emphasized the need to elevate the authority and responsibility of the chief information security officer (CISO) and ensure appropriate investment in security measures.
Each company should upgrade the authority and responsibility of the chief information security officer (CISO) to an vital management level and execute the appropriate investment.
SK Telecom USIM Security Under Scrutiny: Your Questions answered
Published: October 26, 2023 | Updated: November 3, 2023
In the wake of recent security concerns, SK Telecom, a major telecommunications provider in South Korea, is facing increased scrutiny regarding the security of its subscriber identity module (USIM) cards. This article delves into the heart of the issue, providing clear answers to the most pressing questions.
1. What’s the Core Issue with SK Telecom’s USIM Security?
The primary concern revolves around the potential vulnerability of USIM cards to hacking. These cards hold crucial subscriber data, including your IMSI (International Mobile Subscriber Identity) and authentication keys. The core of the current problem, as acknowledged by SK Telecom, is that a portion of this critical USIM information is not fully encrypted. This lack of encryption makes the data more susceptible to interception and misuse by malicious actors.
2. Why is Encryption Vital for USIM Data?
Encryption acts as a digital lockbox for your sensitive data. Without it, information like your IMSI can be accessed relatively easily if a hacker breaches the system. This data can then be used to impersonate you, make unauthorized calls, or gain access to other accounts linked to your mobile number.Encryption safeguards your privacy, prevents identity theft, and protects your overall digital security.
3. What Data is at Risk?
The data at risk primarily includes:
- IMSI (International Mobile Subscriber Identity): A unique number that identifies your SIM card and your mobile phone account.
- Subscriber Authentication Keys: Codes used to verify your identity when connecting to the mobile network.
Access to this information can allow hackers to clone your SIM, intercept your communications, and gain access to your accounts.
4. Has SK Telecom Been Hacked?
While the provided text does not explicitly state that SK Telecom has been successfully hacked, it does mention an investigation into a potential breach and the concerns about the vulnerability of USIM cards. The article highlights hacking events targeting other organizations, such as the harvesting of data from multiple telecom companies and government agencies. The investigation is in the ongoing process of evaluating the extent of the possible intrusion and any ramifications for the security and privacy of user information.
5. What Challenges Exist in Encrypting USIM Information?
One of the biggest hurdles is the need for real-time access to USIM data. As Professor Yeom heung-yeol points out, mobile carrier networks process vast amounts of data constantly. Implementing encryption can possibly slow down these processes,impacting network performance. Finding the right balance between robust encryption and maintaining network speed is a significant challenge.
6.What Do Experts Suggest to Improve Security?
Experts like Professor Yeom Heung-yeol advocate for several key changes:
- Partial Encryption: Encrypting as much data as possible, even if a complete encryption isn’t promptly feasible. Computational performance has been improving, making partial encryption more practical.
- government Oversight: Incorporating mobile carrier servers into government security analyses through revisions to existing laws (like the Information and Interaction-based Protection Act).
- Increased Investment: Carriers need to significantly increase their investments in information security, a point directly contrasted with SK Telecom’s current marketing investments.
- Elevated CISO Authority: The Chief Information Security Officer (CISO) needs increased authority and duty to effectively manage and implement security measures.
7. What’s the Role of Legal Compliance in Addressing the Vulnerabilities?
Current laws don’t definitively mandate encryption for the sensitive information, such as the IMSI and authentication keys, on USIM chips. This legal ambiguity makes the necessity and implementation of security measures uncertain. This situation highlights a need for legal standards that mandate and enforce minimum security criteria for mobile carriers to protect client data.
8. Is SK Telecom Infrastructure Considered ‘Major Infrastructure’?
Currently,SK Telecom’s infrastructure,which was targeted in any potential hacking attempts,has *not* been designated as a major information and communication infrastructure requiring advanced national protection. Though, the ongoing investigation into the potential hacking may lead to a change in this classification, potentially leading to increased security measures and oversight of their operations.
9. How Does Investment in Security Compare to Other Spending?
A major point of criticism is that SK Telecom’s spending on information security is dwarfed by its marketing expenditures. For example, the company spent significantly more on marketing, including promotional campaigns, than on securing its data infrastructure. This disparity suggests an investment imbalance that, according to critics, needs to be corrected.
10. What’s the Impact of the ISun Data Harvest on the Broader Landscape?
The leaked document from Chinese security firm ISun reveals a concerning trend: the increasing vulnerability of major telecommunications companies and government institutions to hacking. The harvesting of 3 terabytes of customer call records from LG Uplus highlights the scale of the threats faced by carriers, underscoring the increasing opportunities for hackers with the expansion of information technology.
11.What are the Specific Actions SK Telecom Is Taking?
An exact list of actions isn’t provided in the text. However, the article mentions that the vice president, Ryu Jung-hwan, acknowledged the issues before the National Assembly and that advisors are being consulted. It also refers to measures that are currently being created.
12. In a Nutshell, What’s the Takeaway?
The core takeaway is that SK Telecom, like other carriers, needs to prioritize data security. This situation underscores the need for improved encryption,increased investment in security infrastructure,greater government oversight,and a stronger emphasis on CISO authority. Ultimately, the security of your personal information—and the trust you place in these providers—are at stake.
Disclaimer: This article is for informational purposes only and should not be considered legal or financial advice.The information provided is based on the source material and is subject to change as new information becomes available.
Sources: Based on the provided content.