
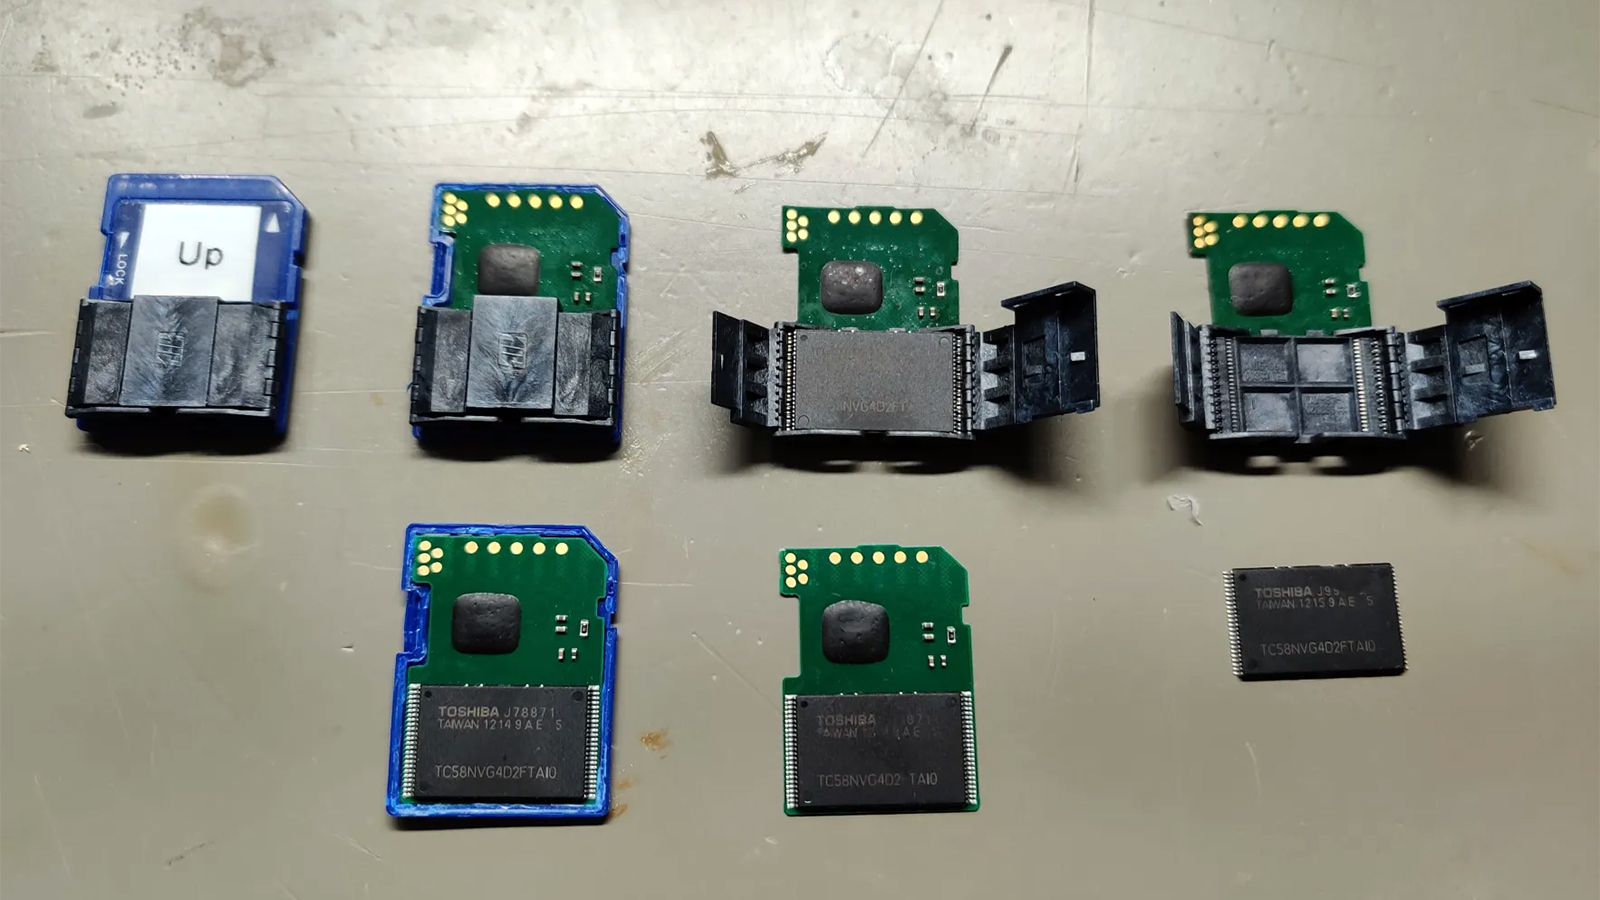
Wii U Boot Exploit: SD Card Repair Reveals Powerful Hack
Wii U Homebrew Community Unveils “paid the beak”: A lifeline for Bricked consoles
Table of Contents
The vibrant and persistent Wii U homebrew community has onc again demonstrated its ingenuity, developing a powerful new tool named “paid the beak” that offers a remarkable solution for recovering Wii U consoles suffering from software bricks. This exploit, born from meticulous data analysis and a deep understanding of the Wii U’s boot process, promises to breathe new life into consoles previously deemed unrecoverable.
Unearthing the SDBoot1 Vulnerability
The breakthrough hinges on a vulnerability known as SDBoot1, a flaw initially identified during the Wii U’s factory setup. This critical discovery allows homebrew developers to execute their own code at the earliest stages of the console’s boot sequence. The “paid the beak” exploit, developed by a member of the group known as Rairii, leverages this vulnerability to bypass standard boot procedures.
The exploit’s code was made publicly available on GitHub, providing a resource for those seeking to revive their beloved Wii U consoles. The advancement process involved a thorough examination of dumped data, with Rairii playing a pivotal role in uncovering the SDBoot1 image and afterward crafting the exploit.
How “paid the beak” Works and Who It Can Save
What makes “paid the beak” particularly significant is its ability to function even on Wii U consoles with completely wiped flash memory. This means that a vast majority of software-bricked consoles can potentially be salvaged. The only exceptions are those devices that have encountered issues with their Seeprom or have suffered actual hardware failures, which are beyond the scope of software-based recovery.
However, it’s important to note that triggering the exploit isn’t entirely plug-and-play. Users will still require specific hardware to initiate the process. This includes either a rare Nintendo jig,a Raspberry Pi Pico,or a PICAXE 08M2 microcontroller. These devices are used to trigger a specific power state, known as UNSTBLPWR, which forces the Wii U to boot from an SD card.
The Recovery Process: A Step-by-Step Guide
Once the necessary hardware is in place and the “paid the beak” exploit is loaded onto an SD card,the recovery process can begin. The user inserts the prepared SD card into their Wii U, utilizes the required jig or choice to trigger the UNSTBLPWR state, and then powers on the console.If successful, the Wii U will boot from the SD card, loading the exploit and opening the door to further system recovery and modification.
This method considerably lowers the barrier to entry for Wii U hardware enthusiasts. It eliminates the need for complex console disassembly and intricate soldering skills,making advanced homebrew experimentation more accessible to a wider audience.
alternatives and the Future of wii U Homebrew
While “paid the beak” offers a powerful solution for software bricks, another mod chip, known as defuse, can also perform similar recovery functions. Notably, deFuse is capable of addressing Seeprom failures as well, though it demands a higher level of technical expertise and knowledge to implement.
The ongoing development and sharing of tools like “paid the beak” underscore the resilience and creativity of the Wii U homebrew community. These efforts not only preserve the legacy of the console but also empower users to explore its capabilities in new and exciting ways, ensuring that the Wii U’s potential can continue to be realized.
**
Follow Tom’s Hardware on Google News to get our up-to-date news, analysis, and reviews in your feeds. Make sure to click the Follow button.*