
Docker Commits Sandbox Kit Spec to CNCF
- Docker and the Cloud Native Computing Foundation are partnering on an open specification to make artificial intelligence agent permissions portable across different runtimes.
- A Sandbox Kit packages an AI agent, its tools, and a typed list of permitted resources into an ordinary Open Container Initiative image.
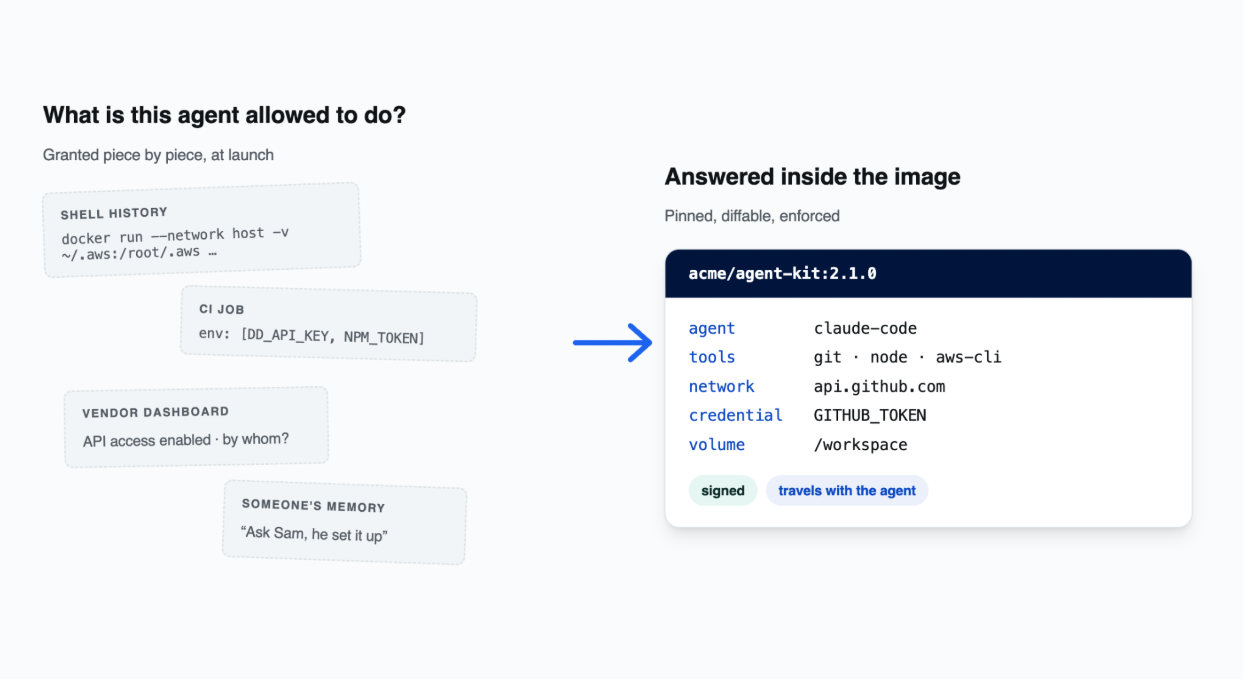
- Standard container images tell runtimes how to start software, but they lack mechanisms to declare permitted network calls, credentials, or file persistence between runs.
Docker and the Cloud Native Computing Foundation are partnering on an open specification to make artificial intelligence agent permissions portable across different runtimes. Linux.com reported that Docker published the Docker Sandbox Kit Spec under the Apache 2.0 license and committed to contributing the specification to the CNCF for neutral governance.
Building Sandbox Kits As OCI Images
A Sandbox Kit packages an AI agent, its tools, and a typed list of permitted resources into an ordinary Open Container Initiative image. The permission list includes network hosts, credentials, and volumes, linking the agent and its access rights together inside a single artifact that builds, pushes, pulls, signs, and scans like standard container software.
Docker is turning "what an agent is allowed to touch" into an OCI artifact. Permissions as versioned capabilities. Credentials proxy-managed so the sandbox only sees sentinel values. Conflicting overlays fail instead of silently widening access. The spec is heading to the CNCF,…
Standard container images tell runtimes how to start software, but they lack mechanisms to declare permitted network calls, credentials, or file persistence between runs. Traditional web services relied on launch flags that rarely changed, whereas agents decide at runtime which packages to install, APIs to call, and environments to alter.
Permissions for agents are typically granted manually piece by piece to unblock tasks, leaving access rules scattered across shell history and dashboards. The new OCI-based specification uses existing annotation extension points in image manifests to carry agent requests without altering registries, scanners, or signing tools.
Governance and Industry Adoption
Chris Aniszczyk, CTO of the CNCF, stated that standards allow ecosystems to move fast without fragmenting. By delivering Sandbox Kits as standard OCI images, Docker is giving the industry an open, repeatable way to package an AI agent, its tools, and its guardrails as one artifact,
Aniszczyk said.
OCI is the foundation the cloud native ecosystem is built on, so a standard for agents that builds on OCI reaches the whole ecosystem at once. The CNCF welcomes this, and we’re excited to work with Docker and the community on making it broadly adopted.
Chris Aniszczyk, CTO of the CNCF
Kits originated as a feature of Docker Sandboxes, which run agents inside isolated microVMs. Docker Sandboxes currently serves as the first runtime that enforces the new specification.
Ecosystem Availability and Developer Tools
Kits for tools from AWS, Box, Datadog, Dynatrace, JFrog, NanoClaw, OpenClaw, Palo Alto Networks, and Snyk are available to cover cloud, observability, security, and artifact management platforms. Database vendors, agent makers, and internal platform teams can publish Kits to establish recommended scopes and uniform starting points for engineers.
Docker encourages developers of agent tools to publish Kits and asks users to share them within their teams. The specification, capability pages, and worked tours are hosted at docker/sandbox-kit-spec.